FCA Crypto Authorization Application Process
Learn the FCA crypto authorization application process, key deadlines, and requirements for UK crypto firms under the new regulatory framework.
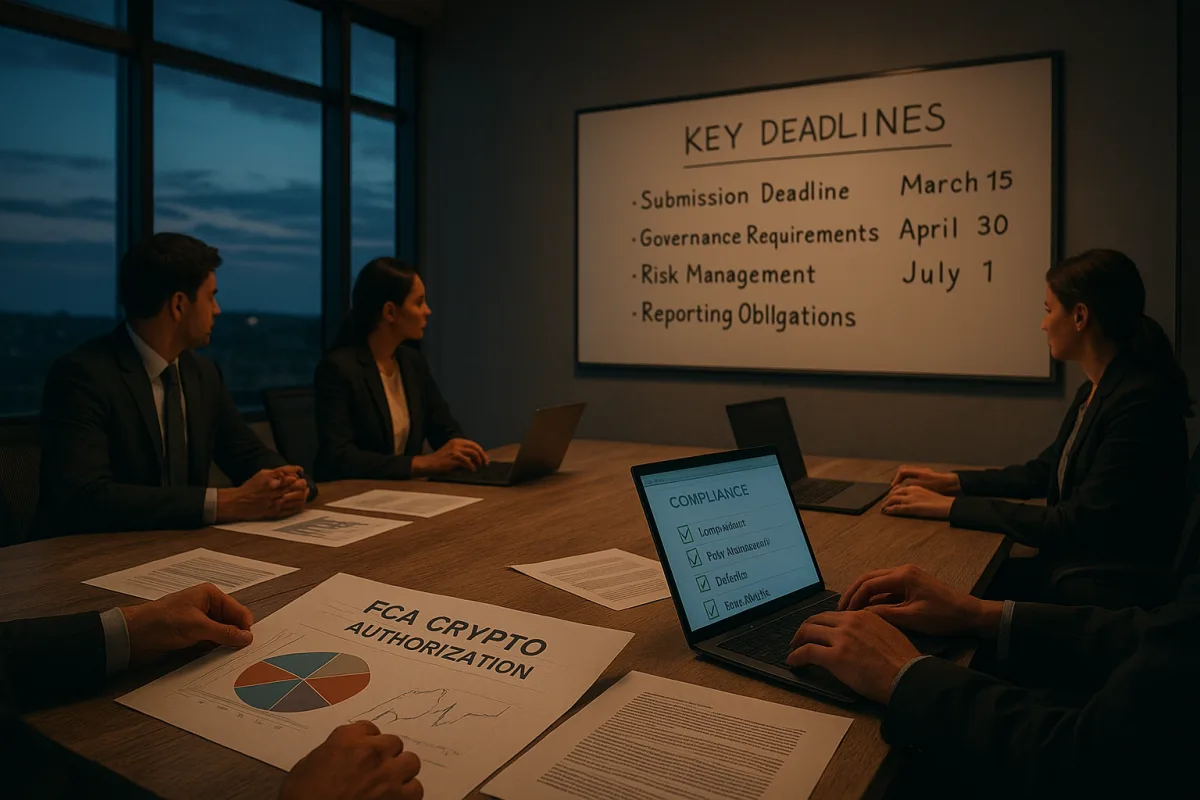
Start by deciding whether the gateway applies to your business
The UK Financial Conduct Authority opened its cryptoasset authorisation gateway on 30 September 2026, giving firms until 28 February 2027 to apply before the broader regime takes effect on 25 October 2027. [5][6] The immediate cost is not a disclosed licence price, but a five-month compliance timetable.
The principal risk is assuming current status carries forward. Firms already registered under the FCA’s anti-money-laundering regime must still make a fresh application through the Financial Services and Markets Act gateway, with no automatic conversion into full authorisation. [4][5]
The first practical task is to map every UK-facing activity against the proposed regulated activities, rather than describing the company with broad labels such as exchange, wallet or infrastructure provider. The FCA regime covers operating trading platforms, dealing, safeguarding, staking and issuing qualifying stablecoins. [5][6]
That exercise matters because corporate structures often separate functions that customers experience as one service. A platform may operate a venue, execute orders, hold client cryptoassets and offer staking, each of which can create a distinct regulatory question under the new framework. [5][6]
Firms should document where the customer is located, which legal entity contracts with that customer, where assets and keys are controlled, and which entity makes trading or custody decisions. These are the operational facts an authorisation case needs to establish, not marketing descriptions of a global platform. [4][5]
Do not rely on the label “non-custodial” without examining the actual permissions architecture. If a business can move assets, alter permissions, intermediate transactions, or exercise practical control over client cryptoassets, it should obtain specialist legal analysis of whether safeguarding rules apply. [4][7]
Work backwards from the February deadline
The deadline is 28 February 2027, but a firm should not treat that as the date to start assembling evidence. CoinDesk described the application period as a five-month process, short relative to the amount of governance and systems work the framework requires. [1][5]
Begin with an accountable owner for the authorisation programme, ideally someone able to obtain decisions from the board, product, engineering, finance, compliance and operations teams. The application will be weaker if it describes policies that no operational team has implemented. [4][6]
Build a regulated-activity inventory first, then assign every activity to a legal entity, customer type, jurisdiction, product flow and control owner. This provides the factual base for determining the permissions sought and identifying activities that need to be paused or redesigned. [4][5]
Next, prepare a gap register that distinguishes documents already in place from controls that operate in practice. Policies for anti-money-laundering, conflicts, incident management or custody are not substitutes for evidence that staff follow them and management reviews exceptions. [4][6]
The FCA has not disclosed how many firms have applied since the gateway opened, so there is no evidence that an early application improves approval odds. [1][5] Early preparation is still practical because it gives firms time to correct defects before the deadline.
Applications need to be complete enough to withstand questioning, rather than rushed merely to secure a place in a queue. The available reporting does not establish an approval-rate forecast for the new regime, and firms should be cautious about consultants presenting one as a fact. [2][3]
Historical registration outcomes illustrate the execution risk, not a forecast of 2027 decisions. Of 391 crypto registration cases reviewed through 1 August 2026, 67% were withdrawn, 17% ended in full registration and 4% in refusals. [2]
Those figures concern the earlier registration framework, chiefly focused on financial-crime controls, and cannot be translated mechanically into a probability of authorisation under the new rules. Another analysis reported a 56% registration rate, underlining how outcome metrics can differ according to the cases counted. [3]
Fix the controls most likely to delay an application
Past FCA scrutiny makes anti-money-laundering controls an early priority. The research record identifies inadequate AML arrangements as a recurring reason for rejection or withdrawal, including the FCA’s March 2025 refusal of Zeux Limited. [2][4]
A practical response is to test the customer journey rather than simply update an AML manual. Record how the firm verifies identity, assesses risk, screens sanctions exposure, monitors blockchain and transaction activity, investigates alerts, and escalates suspicious activity. [4]
The evidence should show where automated tools end and human judgement begins. Firms should be able to explain alert thresholds, false-positive handling, outsourced-provider oversight, management information and how compliance teams can challenge commercially valuable customers. [4]
Operational readiness is the next likely pressure point. The FCA’s framework requires firms to demonstrate financial resilience, appropriate governance and controls, while reporting on the new regime highlights capital, cyber security and internal-control weaknesses as common shortcomings. [4][5][6]
That means preparing a credible wind-down and stress-testing package, not merely a balance-sheet snapshot. Management should model operational disruption, cyber incidents, large customer withdrawals and vendor failures, then show who decides what happens when resilience thresholds are breached. [5][6]
Board materials should identify senior responsibility for each regulated activity, conflicts of interest and risk acceptance. A firm that relies on a parent company, offshore technology team or related-party liquidity provider should make those dependencies explicit and explain their controls. [4][6]
Market-integrity arrangements require similarly concrete work. The incoming rules cover insider dealing and market manipulation, so trading venues and brokers need surveillance, escalation and recordkeeping procedures that match how orders, listings and token launches actually occur. [5][6]
It is not enough to state that blockchain transactions are public. Public ledgers do not automatically identify beneficial owners, coordinated trading or internal access to market-sensitive information, which are the practical issues a market-abuse framework must address. [6]
Treat custody as a client-assets and insolvency issue
Safeguarding may be the most consequential redesign for firms holding customer cryptoassets. Under CASS 17.3, a firm safeguarding cryptoassets must hold them on trust for clients, helping protect customer claims from competing claims in the firm’s insolvency. [7]
The immediate work is to identify every wallet, key-management system, omnibus address, third-party custodian and internal ledger that touches client assets. The firm then needs to establish which assets belong to customers, which belong to the firm, and how that distinction is maintained. [7]
A custody design should also account for the difference between blockchain records and internal books. On-chain balances alone may not identify each customer’s entitlement in an omnibus wallet, so reconciliation processes and records of beneficial ownership are central to the safeguarding case. [7]
Document the legal and operational chain where third parties are involved. If assets are held through a sub-custodian, staking provider or technology supplier, the applicant needs to show how client rights, withdrawal access, reconciliation and failure procedures remain protected. [4][7]
Firms offering staking should not assume the service is outside custody obligations because assets are delegated or locked through a protocol. Staking is included among the activities addressed by the UK framework, and the service design needs to show what happens to customer rights and assets. [5][6]
Build the stablecoin case separately
Issuers of qualifying stablecoins should prepare a separate workstream instead of treating the token as a minor extension of an exchange product. The UK framework addresses stablecoins designed to maintain a stable value by reference to a currency, with transparency and consumer-protection expectations. [5][6]
That calls for clear disclosure of the stabilisation mechanism, reserve arrangements, redemption process, custody of backing assets and governance over changes. It also requires firms to test what happens when redemptions rise sharply or a banking, custody or operational counterparty fails. [5][6]
The UK approach should not be assumed equivalent to the European Union’s Markets in Crypto-Assets regime. MiCA has applied to service providers since 2024, whereas the FCA regime is UK-only and uses its own activity-based structure and application timetable. [5][6]
MiCA addresses cryptoasset service providers and issuers of asset-referenced and e-money tokens across the EU. The FCA’s framework instead focuses, among other areas, on qualifying stablecoins, trading, dealing, safeguarding and staking within the UK perimeter. [5][6]
A firm operating in both markets should therefore maintain a jurisdiction-by-jurisdiction permissions map. A MiCA authorisation, transition plan or compliance programme may provide useful operational material, but it does not remove the need to satisfy the FCA’s separate authorisation process. [4][6]
Avoid making claims the evidence does not support
The gateway opening is a regulatory milestone, but it is not evidence of an imminent increase in UK crypto trading volumes, token issuance or investment. No public data currently shows the number of applications submitted or authorisations granted under the new window. [1][5]
It is also too early to claim that property-law reform has produced measurable market benefits. The Property (Digital Assets etc.) Act 2025 received Royal Assent on 2 December 2025, following the Law Commission’s recommendation to recognise digital assets as personal property. [8]
That legal development may help clarify ownership disputes, but there is no identified quantitative evidence linking it to higher crypto volumes, reduced disputes or improved market confidence. The Court of Appeal’s February 2026 ruling that Old School RuneScape gold can be property illustrates legal recognition, not crypto-market impact. [8]
For applicants, the more immediate commercial question is whether their control environment can support UK operations after October 2027. The FCA’s stated objectives include stronger consumer protections, client-asset safeguards, market integrity and financial resilience, all of which require evidence rather than forecasts. [5][6]
Frequently Asked Questions
How do crypto firms apply for FCA authorisation in the UK?
Firms must submit a fresh application through the Financial Services and Markets Act (FSMA) gateway, even if they are already registered under the FCA’s anti-money-laundering regime. The process involves mapping all UK-facing activities against the regulated activities defined by the FCA, such as trading platforms, dealing, safeguarding, staking, and issuing qualifying stablecoins. Firms should provide detailed operational facts including customer location, legal entities involved, and control over assets and keys.
What are the FCA requirements for cryptoasset authorisation?
The FCA assesses governance, capital adequacy, operational resilience, market abuse controls, and cryptoasset safeguarding arrangements. Firms must demonstrate financial resilience through adequate capital and stress testing, comply with market integrity rules, and establish organisational arrangements to protect client rights in insolvency. Safeguarding cryptoassets requires holding them on trust for clients under CASS 17 rules.
When is the FCA crypto authorisation application deadline?
The deadline to submit an FCA authorisation application is 28 February 2027. Firms intending to carry on regulated UK cryptoasset activities after the regime begins on 25 October 2027 must apply by this date.
What governance and controls does the FCA assess in crypto applications?
The FCA evaluates a firm’s governance structures, capital resources, operational resilience, controls against market abuse, and arrangements for safeguarding cryptoassets. This includes ensuring firms have appropriate internal controls, cybersecurity measures, and that safeguarding is treated as both a legal-structure and custody issue to protect client assets.
How should firms prepare for the FCA crypto regulatory gateway?
Firms should start well before the February 2027 deadline, as the application process can take around five months and requires extensive governance and systems work. Preparation involves thoroughly documenting all regulated activities, legal entities, control points, and client interactions, as well as building robust compliance controls and safeguarding frameworks rather than simply completing an application form.
How we researched this
This article was assembled from 3 published articles, 8 cited references.
Nothing here is based on hands-on testing. Where a figure or finding appears, it belongs to the source cited beside it, and the writing says so rather than implying otherwise. Every source is listed below so you can check it.
Sources
FCA starts accepting crypto authorization applications ahead of 2027 regime — The Block
Clock's ticking: UK's crypto regulatory application window opens with February deadline — CoinDesk
UK Brings Crypto Under Full FCA Oversight for the First Time — Bitcoin Magazine
FCA starts accepting crypto authorization applications ahead of 2027 regime | The Block
Most crypto firms will not clear FCA authorisation - Fintechly
FCA Crypto Registration Rate Hits 56%, But Context Matters » HashLytics
FCA Cryptoasset Authorization: What Firms Need to Know Before the 2026 Gateway Opens
New bill introduced in Parliament to clarify crypto’s legal status - GOV.UK
Related Articles
CLARITY Act Crypto Ethics Provision and Senate Vote Update
Explore the CLARITY Act's crypto ethics provision, enforcement challenges, and Senate vote status affecting federal officials and digital assets.
Stablecoin and Tokenized Securities Developments Explained
Explore stablecoin reserve models, ECB's Pontes system, and tokenized securities infrastructure in the latest regulatory and market developments.
Crypto Regulatory Challenges
Explore crypto regulatory challenges, legal risks, and compliance costs shaping stablecoins, blockchain records, and cross-border crypto markets.
Bitcoin-Backed Mortgages and Crypto Credit Lines Explained
Learn how Bitcoin-backed mortgages and crypto credit lines work, their collateral needs, risks, and custody details for U.S. borrowers.